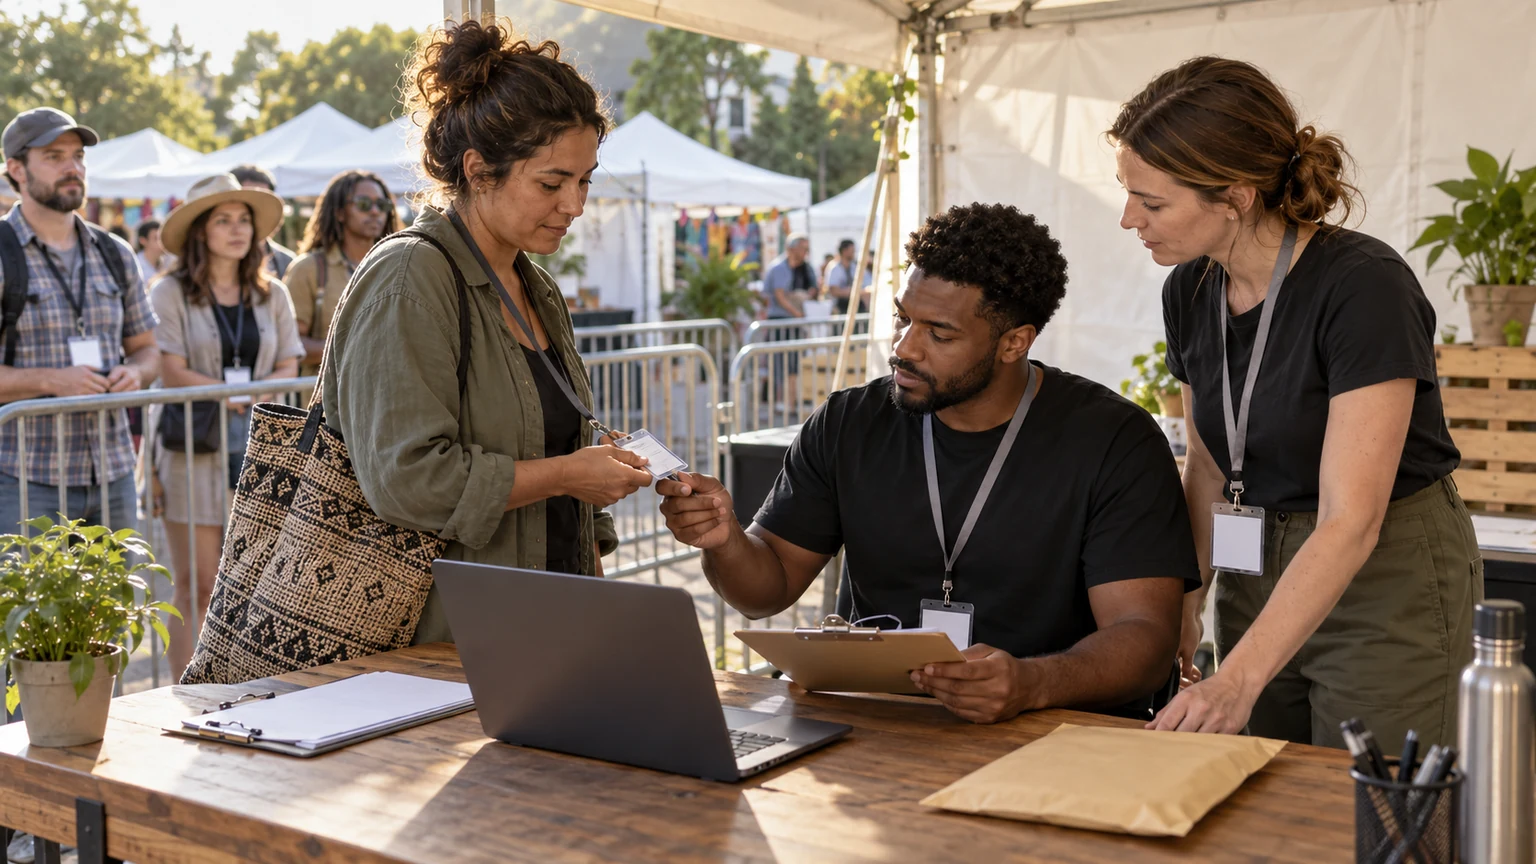
A reported police warning about a festival vendor registration scam is a useful reminder for organizers, festival planners, and operations teams.
On its own, that public warning does not give us a full incident report, a universal scam pattern, or a complete prevention framework for every event type. But it does point to something operationally important: vendor registration is not just a form and a payment link. It is a risk-control process.
For festivals and fairs, that matters because vendor scams can damage trust on both sides. Organizers may lose credibility, and legitimate vendors may lose money, time, or access to the event.
If vendor registration is easy to spoof, it is also easy to misuse.
Why this matters
Many event teams focus security attention on ticketing, attendee entry, and on-site safety. Those are important. But vendor operations also create exposure.
Common risks include:
- fake registration outreach sent to prospective vendors
- fraudulent payment requests using event branding
- impersonation of event staff or partner organizations
- duplicate or unofficial application pages
- unclear approval processes that create room for confusion
- last-minute changes communicated through unverified channels
These problems are not only financial. They can lead to angry vendors, overloaded staff, disputed payments, and avoidable reputational harm shortly before showtime.
What the public signal actually tells us
From the information available here, the confirmed signal is limited but useful: police in Saskatoon reportedly warned of a festival vendor registration scam.
That is enough to support a practical discussion about how organizers can reduce vendor registration risk.
What it does not confirm on its own is:
- the full scam method used in every case
- whether the scam targeted one event or multiple events
- which controls were already in place
- how vendors first encountered the fraudulent outreach
- which prevention steps would have stopped each attempt
That distinction matters.
A police warning is a strong signal to review process controls, not proof that every vendor workflow is broken in the same way.
Treat vendor registration as a controlled workflow
The safest starting point is simple: define one official vendor registration path and make it easy to verify.
That means documenting:
- where applications begin
- which email domains are official
- who is authorized to contact vendors
- when invoices are issued
- how payments are collected
- what confirmation messages vendors should expect
If your own process is inconsistent, fraudsters have more room to imitate it.
Use one clear source of truth for vendors
Vendors should never have to guess where the real process lives.
Create one official page for vendor information and keep it updated throughout the event cycle. That page should state:
- the official application window
- the approved contact email or emails
- whether outreach to vendors is proactive or application-based
- accepted payment methods
- whether invoices come from the organizer directly
- how vendors can verify suspicious messages
If you use social media or community groups to promote vendor opportunities, every post should point back to that same official page.
Lock down payment handling early
Payment confusion is often where scams become expensive.
Before registration opens, decide exactly how money will move and who controls each step. Keep the process narrow.
A practical model includes:
- application submission through the official channel
- internal review and approval
- formal acceptance notice
- invoice or payment request sent through the approved system
- payment confirmation from the same verified source
Try to avoid ad hoc exceptions unless they are documented and approved. The more payment routes you allow, the harder it becomes for vendors to spot fraud.
Make staff identity easy to verify
Impersonation works best when vendors do not know who is real.
Help vendors verify communications by standardizing your outbound contact details:
- use consistent sender names
- send from official domains only
- list named staff on the vendor information page
- publish a phone number or verification email for suspicious requests
- avoid collecting payment details through informal messages
If temporary staff or external contractors support vendor operations, define exactly what they can and cannot send.
Build warnings into vendor communications
Do not assume vendors will recognize a scam on their own.
Add a short security note to vendor-facing emails and application pages. For example, tell vendors:
- never to pay through unlisted channels
- to verify any change in payment instructions
- to ignore unofficial social media direct messages
- to confirm suspicious invoices before paying
- that official communication comes only from named sources
This is a small operational step, but it can reduce confusion significantly.
Review where fraud can enter the process
Most vendor scams do not require a technical breach. They exploit weak communication design.
Walk through the full vendor journey and ask where a bad actor could insert themselves:
- during vendor recruitment
- after inquiry but before approval
- between acceptance and payment
- during booth assignment or logistics updates
- close to event day when urgency is high
That review often reveals simple fixes, such as better wording, fewer handoffs, or clearer timing.
Create an escalation path before you need it
If a vendor reports suspicious outreach, staff should know what happens next.
Define an internal response path that covers:
- who receives the report first
- who verifies whether the message is fraudulent
- how quickly vendors should get a response
- whether legal, finance, or venue partners need to be informed
- when a public warning should be issued
Speed matters. A slow response can allow the same scam to reach more vendors.
Train for exceptions, not just the happy path
Vendor registration problems usually surface when something changes: a deadline extension, a waitlist opening, a booth reallocation, or a payment issue.
These moments create pressure and confusion, which is exactly when fraudulent outreach can look believable.
Prepare staff with simple rules for exception handling:
- all exceptions must still use official channels
- payment instruction changes require extra verification
- booth or status changes should be confirmed in writing
- urgent requests should not bypass approval controls
Consistency is a security tool.
A compact checklist for organizers
- publish one official vendor registration page
- list official staff contacts and communication channels
- use one approved payment process
- warn vendors explicitly about impersonation and fake invoices
- standardize outbound email names and domains
- define an internal escalation process for suspicious reports
- review exception handling before registration opens
- repeat the verification message across web, email, and social posts
What organizers should not assume
It is easy to assume that a scam only works when organizers have no process at all. In practice, even legitimate events with real vendor demand can be imitated.
It is also risky to assume that one website notice is enough. Vendors often encounter an event through shared posts, community groups, or forwarded messages, not only through the official site.
And do not assume that security is only a technical problem. In many cases, the weakness is operational: too many channels, unclear ownership, inconsistent messaging, or rushed payment handling.
What this means for event teams
The practical lesson is not to make vendor registration harder. It is to make it clearer, narrower, and easier to verify.
For festivals and fairs, strong vendor security starts with process discipline: one source of truth, one approved payment path, clear staff identity, and fast response when something looks wrong.
That approach protects vendors, reduces staff friction, and helps preserve trust in the event long before opening day.