Private event access often fails in ordinary ways.
Someone forwards the link. A guest uses the wrong email. A VIP arrives without the original invite. Staff cannot tell whether a person should have access, and the event that was meant to feel controlled starts to feel improvised.
The source idea behind this topic is practical and narrow: for private events, simply telling people to share a URL is usually not enough. That is enough to discuss better access patterns for organisers without claiming one universal model, one legal standard, or one product-specific workflow.
For a private event, the join path is part of the operations plan, not only a convenience for attendees.
Why this matters for event operations
Private access sounds simple until the audience starts moving through it in real conditions.
Teams may be trying to control entry for:
- client events and hosted dinners
- member-only gatherings
- internal company events
- partner sessions at larger conferences
- private previews, launches, or invite-only receptions
- small paid events that should not circulate publicly
In each case, the access model affects more than registration. It shapes guest confidence, support workload, on-site check-in, and how exposed the event becomes to the public internet.
If the only plan is “send the link,” familiar problems appear fast:
- uninvited people find the page
- invited guests are unsure whether they are properly registered
- staff have no clean way to confirm who belongs there
- support requests increase close to the event
- access rules are applied inconsistently
- the event feels less private than intended
What we can say, and what we cannot
Based on the source idea, it is reasonable to say that private event access usually needs more structure than an open link alone.
It is also reasonable to say that invite emails, join codes, and simple access checks can reduce confusion when they are planned properly.
What we cannot claim from the source alone is that any single method is always best, that one setup prevents all sharing, or that every private event needs the same level of restriction.
That matters because a board dinner, a member webinar, and a private festival afterparty do not carry the same access risk or guest expectations.
The right access model depends on the event’s privacy needs, guest mix, and check-in realities, not on habit.
Start with the actual privacy level of the event
Many access issues begin because teams say an event is private without defining what that means operationally.
Ask a more specific question: what exactly are you trying to control?
Usually that means one or more of the following:
- keeping the event page out of casual public discovery
- limiting who can register
- making sure each invite is used by the intended guest
- controlling plus-ones or guest substitutions
- preventing capacity from being taken by the wrong audience
- giving staff a reliable check-in list
Once that is clear, the join path becomes easier to design. Without that step, organisers often choose a setup that is either too loose or too burdensome.
Why “send the link” is usually too weak on its own
A direct URL can be useful. It is simple, fast, and easy to distribute. The problem is treating it as the whole access strategy.
A link by itself does not answer several operational questions:
- Who is allowed to use it?
- Can it be forwarded?
- How will staff distinguish invited from uninvited guests?
- What happens if someone registers with a different email address?
- How will late additions or replacements be handled?
- What should the guest experience be if access fails?
When those questions are unresolved, the link becomes a source of ambiguity rather than simplicity.
Build the join path around guest recognition
Private event access works better when the system can recognise the guest in a deliberate way.
That does not always mean heavy verification. It means giving the event a practical method to connect the invitation, the registration, and the arrival.
Common patterns include:
- invite email as the access path: useful when the invited list is known and the guest is expected to respond through the same email channel
- join code: useful when guests need a controlled way to access the registration page without making the event broadly public
- named guest list checks: useful when access decisions are managed manually or through a tightly controlled attendee list
- combined approaches: useful when the event needs both a simple guest experience and more control behind the scenes
The point is not to make entry feel difficult. It is to make access rules legible to both guests and staff.
When invite emails work best
Invite emails are often the cleanest option for truly private events because they give organisers a direct, intentional path to the attendee.
They are especially useful when:
- the guest list is curated in advance
- capacity is limited
- the event has hosted or VIP elements
- the organiser needs clearer response tracking
- guests are expected to arrive under their own name, company, or invitation status
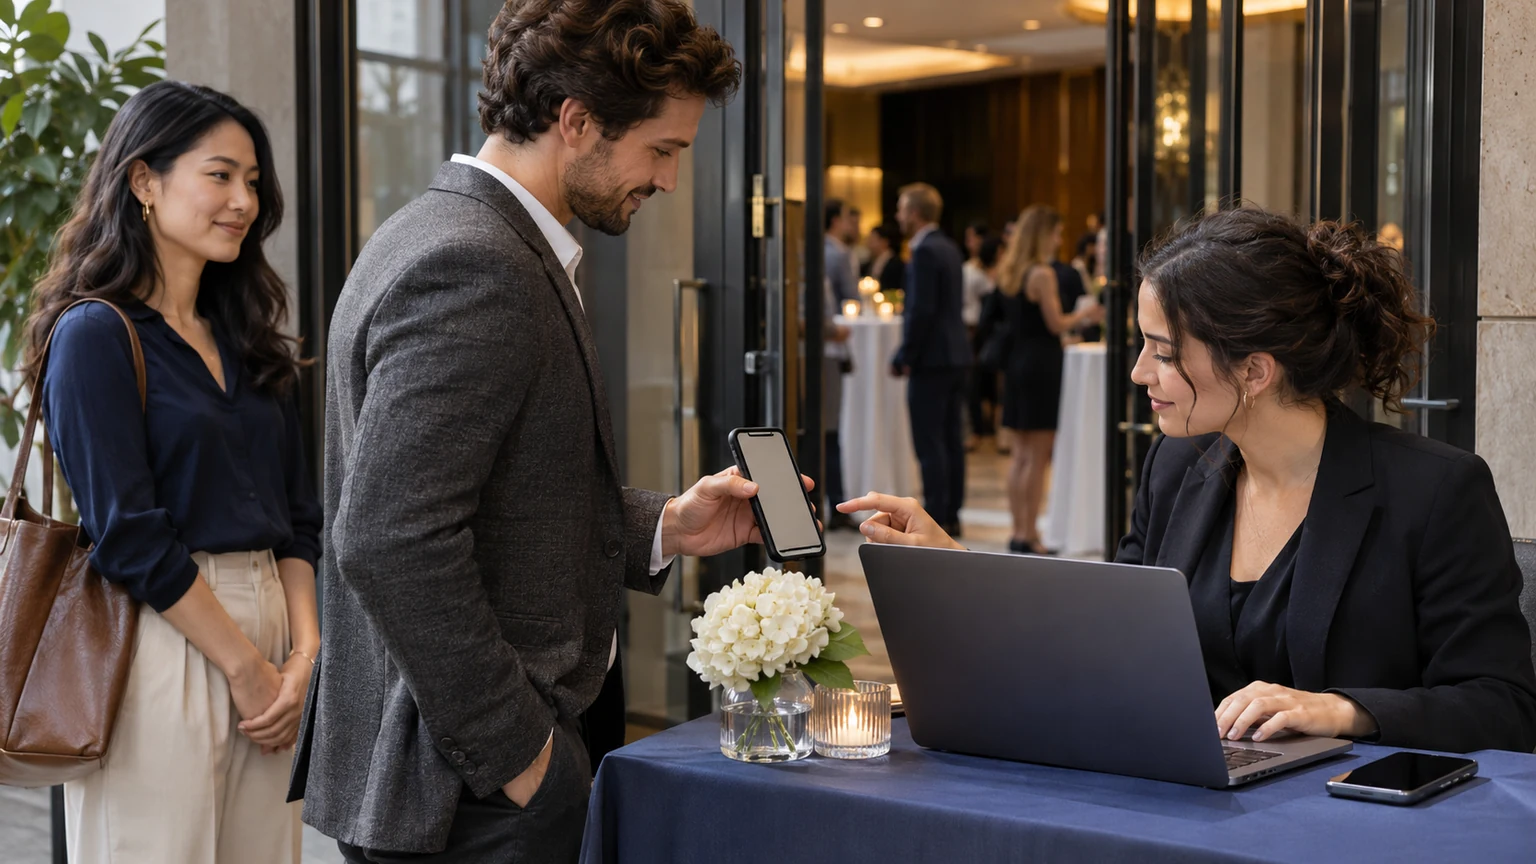
Operationally, invite emails help because they create a visible record of who was asked, who responded, and who may need follow-up.
They also reduce the chance that a private event looks like an open public listing with a thin layer of language on top.
What teams should still watch for
- guests using a different email from the invited one
- assistants registering on behalf of senior attendees
- forwarded invites that create confusion at check-in
- last-minute substitutions that have not been updated internally
These are manageable issues, but only if the team expects them in advance.
When join codes are useful
Join codes can help when organisers want access to feel straightforward without leaving the event exposed to general browsing or accidental sign-up.
They are often useful when:
- the audience is private but not individually curated down to every recipient
- multiple guests may be invited through one organisation, team, or community
- the event needs a cleaner gate than a public registration page
- the organiser wants a simple way to control circulation
A join code is not magic. People can still share it. But it introduces an intentional step, which is often enough to reduce casual spread and improve access clarity.
The main operational question is whether staff know how the code relates to guest eligibility. If they do not, the code only moves confusion to a different stage.
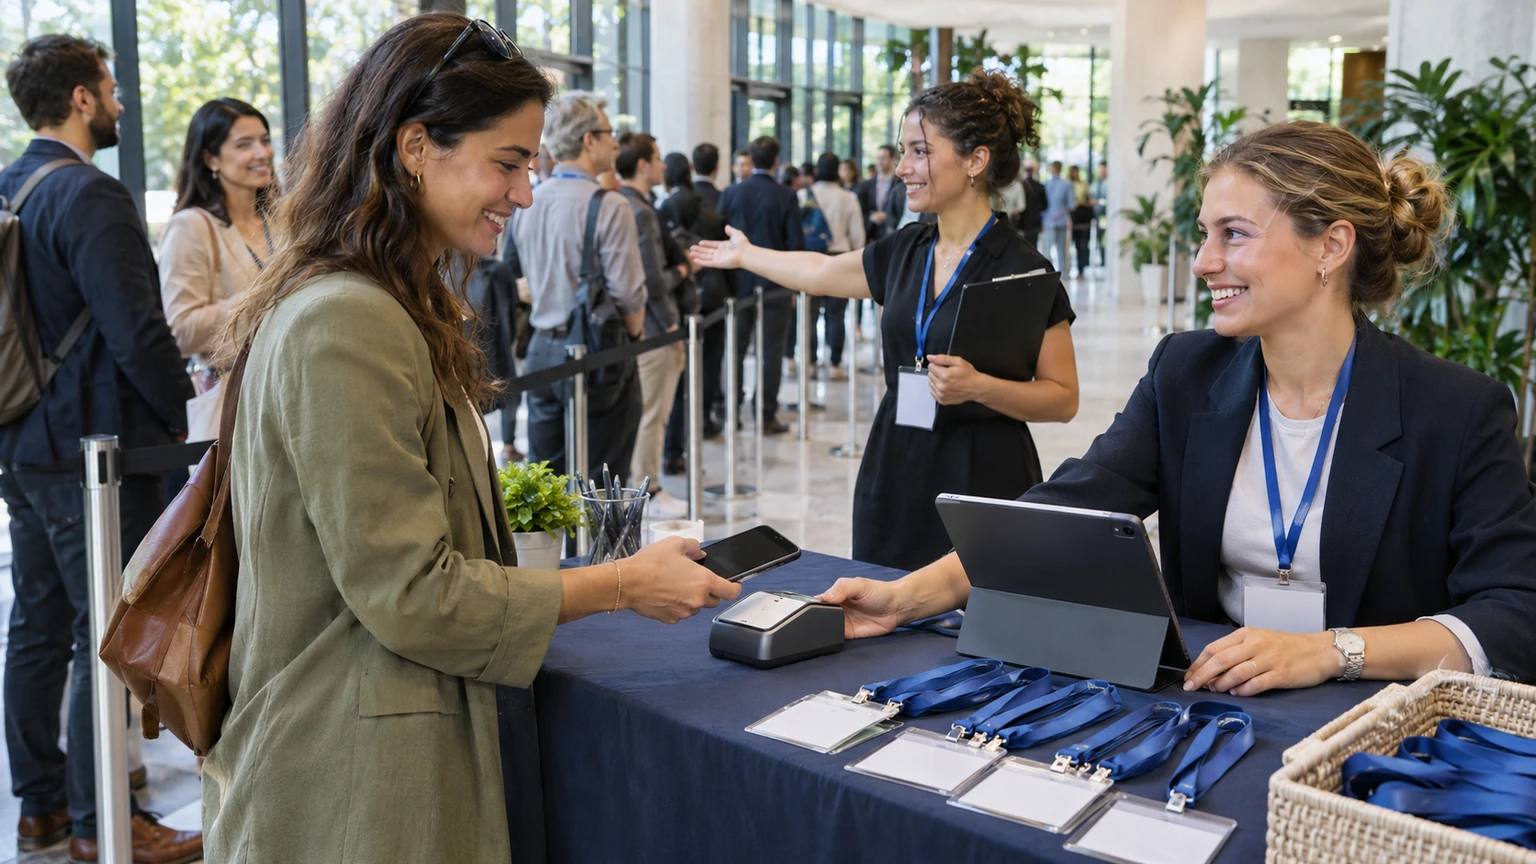
Do not separate access setup from check-in planning
One of the most common mistakes is designing private access only from the registration side.
On-site teams then inherit the consequences.
Before launch, organisers should be able to answer:
- What name will staff expect to see at check-in?
- Will guests show confirmation, identify themselves, or both?
- How will replacements or plus-ones be handled?
- Who can approve exceptions on the day?
- What happens when someone says, “I was invited, but I cannot find the email”?
If the answer to those questions is unclear, private access is not finished, even if the invitation has already gone out.
Keep the guest experience simple
Private should not mean complicated.
The strongest access flows usually feel calm from the guest side. The rules are there, but they are easy to follow.
That usually means:
- one clear route to join
- plain language in the invite
- no unnecessary steps
- confirmation that explains what happens next
- access instructions that match the real arrival process
Guests do not need to see all of the operational logic. They only need enough clarity to trust the process.
A useful test is simple: could a busy invitee understand how to join in under a minute, without emailing for help?
Plan for the edge cases before guests find them
Private events are especially sensitive to edge cases because exceptions often involve important people: hosts, sponsors, speakers, clients, board members, or late-added partners.
Build a short exception plan in advance.
Useful scenarios to cover
- a guest was invited but cannot find the original message
- someone registers with a different email address
- an assistant completed the response for an executive
- a named attendee is replaced close to the event
- a plus-one arrives who was discussed informally but not recorded clearly
- someone has the link but was never meant to attend
These are not unusual failures. They are normal operating conditions for private events.
A practical setup sequence
For most teams, a sensible planning sequence looks like this:
- define what “private” means for this event
- choose the primary access path, invite email, join code, or a combination
- decide how attendee identity will connect to check-in
- write guest-facing instructions in plain language
- prepare an exception process for substitutions and missing invites
- brief front-of-house staff on access rules and escalation points
- test the journey as if you were a guest, not only as an organiser
This sequence is not complicated, but it prevents many of the access problems that appear when privacy is treated as an afterthought.
Where teams should be careful
A few patterns tend to create avoidable friction:
- calling an event private while leaving registration too open
- using codes or invite rules that front-of-house staff cannot interpret
- letting guest substitutions happen informally without list updates
- sending different access instructions across email, landing pages, and reminder messages
- making the process so strict that legitimate guests struggle to enter
The goal is controlled access with low confusion, not maximum restriction for its own sake.
What good looks like
A well-run private access flow has a few clear qualities.
Guests understand how to join. The event is not casually exposed. Staff can see who should be there. Exceptions are manageable. Entry feels deliberate, not defensive.
Most importantly, the organiser is not relying on social convention alone. “Please do not share this link” is not a full operating model.
What this means for event teams
If your private event access plan is only a URL in an email, it is worth tightening the design before launch.
You do not always need a heavy process. But you do need a real one.
Invite emails, join codes, and clear guest recognition rules can make private access feel easier for the right people while keeping the event more controlled for everyone managing it.
That is the real standard to aim for: simple for guests, usable for staff, and private in practice, not only in intention.